Good news, Knicks employees: management has identified a dangerous vulnerability. Some of you still believe it might do something nice for you.
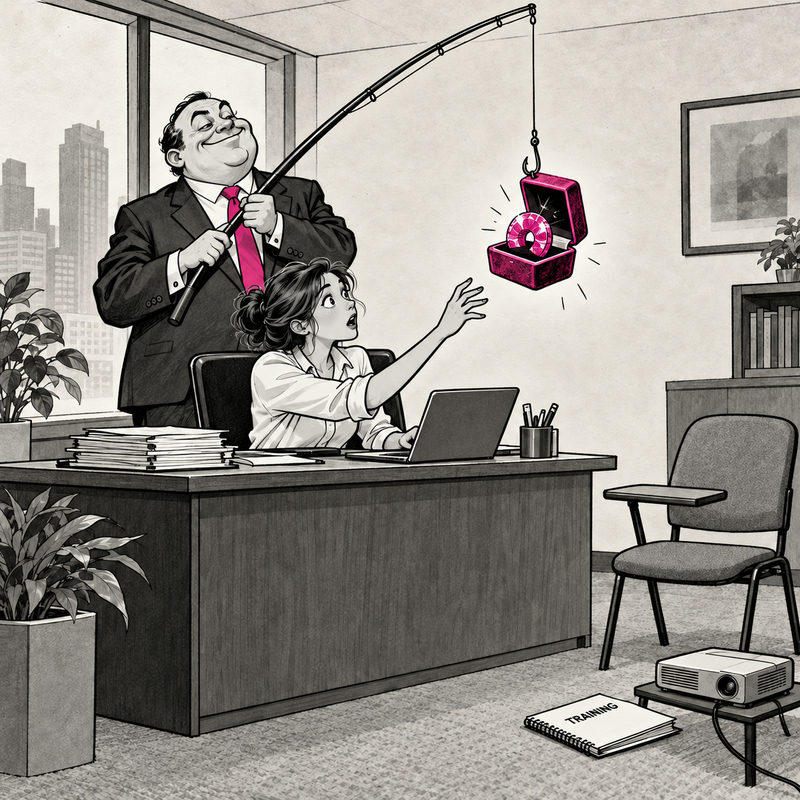
Ars Technica reported Friday, following The New York Times, that a late-September phishing test offered staff championship rings. Employees who clicked reportedly faced mandatory cybersecurity training. MSG confirmed the test, cited a real credential-theft attack and extortion, and called the ring lure an “unfortunate mistake.” It also says real rings and jewelry are going to players, coaches, employees and others. The number who clicked is unknown.
Protecting employee accounts is a perfectly good objective. Turning an apparent thank-you into a trap is an unusually efficient way to protect those accounts from ever being used to express enthusiasm again.
The lesson should be that an unexpected message deserves scrutiny. It should not be that recognition from your employer is inherently too implausible to survive a basic security check.
Make powerful people uncomfortable.
Subscribe to Democrawonk.
There’s a distinction. A suspicious attachment can be inspected. A company culture in which a reward sounds believable only to the dangerously naïve needs a different department.
Imagine the training exercise this creates in a worker’s head. An email promises something good. Was the sender legitimate? Is the link correct? More importantly, have I briefly forgotten where I work?
That last question should not be part of anyone’s threat-detection software.
The point is not to abolish security training. It is to stop treating an employee’s hope for recognition as a particularly useful attack surface.
Security depends on people believing instructions when those instructions matter. Management would therefore benefit from not turning its own apparent generosity into the practical joke employees are expected to spot.
The ring was a test. The way they treated the staff wasn’t.
Comments
Have something to say? Give this story a heckle.
Comment Rules
Argue the point. Add a joke. No threats, harassment, hate speech, spam, private personal information or unsupported accusations. First-time comments and comments with links are moderated. Full Comment Rules
Loading comments…
Questions or deletion requests? Contact Us. We retain comments and moderation records until removed. Only hashed email identifiers are stored for comment accounts.